Service overview
APIs become valuable when they remove duplicate work. If staff are copying customer data, checking payments manually, exporting reports, or moving records between tools, the business is losing time and accuracy.
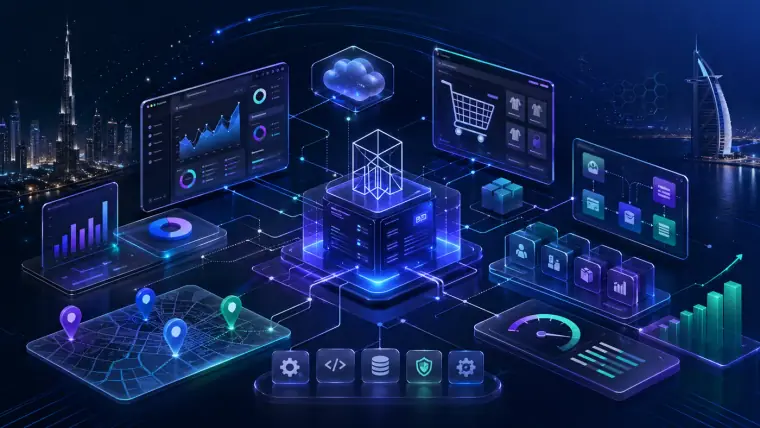
Anas Tanveer provides API integration services for Laravel, WordPress, Shopify, dashboards, CRMs, payment gateways, maps, email tools, webhooks, reporting systems, and custom automation workflows.
This service is useful for businesses that want their website, dashboard, ecommerce store, and internal tools to share data safely and reliably.
What businesses come to me with
- Teams manually copy data between systems, creating delays and mistakes.
- Payment, CRM, email, map, or reporting tools are not connected to the website.
- API failures are not logged clearly, making problems hard to debug.
- The business needs secure data exchange without exposing sensitive information.
What a api integration has to do
Where this pays for itself
- Payment integrations
- CRM connections
- Shopify and ecommerce APIs
- Dashboard data feeds
- Webhook automation
Why work with Anas Tanveer
From first call to live
The integration is planned around data accuracy, permissions, error handling, and the business process. Endpoints, payloads, retries, logs, and admin controls are structured for maintainability.
The result is a connected workflow with less manual effort, cleaner data, faster reporting, and fewer operational gaps between the tools the business already uses.
Anas Tanveer is a Dubai-based full-stack web developer connected with ARS Developer Ltd, working across Laravel, PHP, WordPress, Shopify, React, Next.js, MySQL, REST APIs, SEO, PageSpeed, dashboards, ERP, CRM, and ecommerce systems for UAE, UK, Canada, and international project needs.
The integration is the easy half
Connecting two systems on a good day is straightforward: read the documentation, send the request, parse the response. What separates an integration that runs for years from one that quietly breaks is everything around that happy path — what happens when the other service is down, slow, rate-limited, or returns something the documentation never mentioned.
Assume every external call will fail eventually, because it will. The question a build has to answer is what the business does in that minute: queue and retry, fall back to a cached value, or stop and tell someone. That decision is different for a payment than it is for a shipping rate, and it belongs in the specification rather than in an exception handler written under pressure.
Retries, and the duplicate charge problem
A request that times out has not necessarily failed. It may have succeeded on the other end while the response was lost in transit, and a naive retry then charges the customer twice or creates the order twice. This is the single most common serious bug in integration work.
The fix is idempotency: every outgoing request that changes something carries a key the receiving system uses to recognise a repeat, so retrying is safe. Where a provider does not support idempotency keys, the same protection is built locally — recording the attempt before it is sent and reconciling afterwards, rather than trusting the response alone.
Webhooks over polling, where the provider allows it
Polling an API every minute to see whether anything changed burns rate limit, costs money on metered plans, and still delivers the news up to a minute late. A webhook does the opposite: the provider tells you the moment something happens.
The trade is that webhooks arrive out of order, arrive twice, and arrive when the server happens to be restarting. So they are accepted quickly, stored, and processed separately, with a signature check on every one — an unauthenticated webhook endpoint is a public API for changing your data, and it does get found.
Credentials, sandboxes and the day the token expires
Keys live in environment configuration, never in the repository, and are separated so that a test environment cannot touch live data. Every provider worth integrating offers a sandbox; the ones that do not get a test double so the integration can be exercised without moving real money.
Tokens expire, certificates lapse and providers deprecate versions on their own schedule. The build includes refresh handling and an alert when a credential is close to expiry, because the alternative is discovering it from a customer on a Sunday.
Frequently asked questions
Can APIs connect Shopify, Laravel, and CRMs?
Yes. APIs can connect ecommerce stores, Laravel dashboards, CRMs, payment gateways, email platforms, maps, and reporting tools.
Do API integrations work on static websites?
Static websites can use external form services and third-party scripts, but secure custom API processing usually needs a backend or external service.
What systems can be connected through an API integration?
Common integrations include payment gateways, CRMs, ERPs, shipping providers, email and SMS platforms, maps, accounting tools, and custom internal systems.
How do you handle API security?
Integrations use authentication tokens, secure HTTPS connections, request validation, rate limiting, and careful handling of credentials and sensitive data.